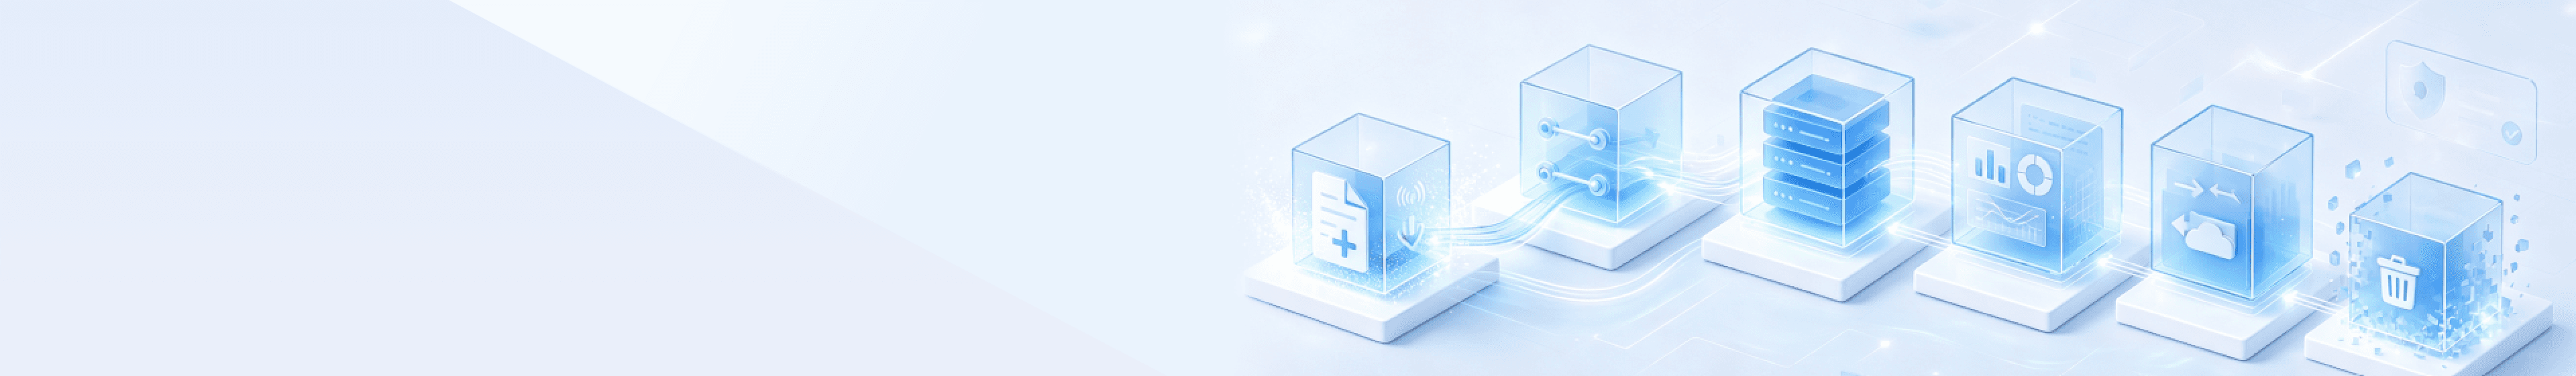
Data lifecycle management covers six key stages from collection
to destruction. Clear control points and standards are defined for
each stage to safeguard data quality, security and compliance
throughout its lifecycle.
Full Data Lifecycle Workflow
Collection
Transmission
Storage
Processing
Exchange
Destruction
Collection
Raw data is obtained via multi-channel collection, manual submission, system integration and bulk import. Initial data validation and formatting are performed to support subsequent business operations and analytics.
▶All data collection activities require prior review to verify business necessity, and strictly mitigate risks of excessive and unnecessary data collection at the source.
Transmission
Data circulation for scenarios including on-campus system interconnection, internal & external interface, and online distribution, covering internal network transmission and cross-institutional transmission over external networks.
▶Data transmission across networks or organizations must be equipped with corresponding security safeguards and encryption controls to prevent intermediate leakage, tampering and hijacking.
Storage
Classified secure storage and protection are implemented for all collected data, ensuring authorized personnel can normally retrieve and access data within the compliant retention period.
▶Data storage shall implement corresponding classified security policies. Comprehensive backup and disaster recovery mechanisms are established to avoid data loss and unauthorized access.
Processing
Diverse data operations including cleansing, computation, processing, desensitization, aggregation, splitting and modeling are carried out to meet demands of business operation, statistical analysis, research and report generation.
▶All data processing must be supported by compliant and legitimate business rationale. Operation logs shall be retained throughout sensitive data processing to enable traceability of every action.
Exchange
Data interaction scenarios including inter-department sharing within the university, submission to external entities, circulation for third-party cooperation and open inquiry, covering internal sharing and external data output.
▶External data exchange follows formal approval procedures with access limited to the minimum necessary scope. Records of all exchange activities shall be maintained to strictly prevent unauthorized outflow of sensitive information.
Destruction
Storage and archived data that is expired, obsolete or retained in violation of rules shall be completely erased in accordance with retention requirements, laws, regulations and university policies.
▶Destruction methods shall match data sensitivity levels to ensure timely and thorough erasure without data residue, eliminating potential privacy leakage risks.